Access based on identity and context
Connect users, groups, posture and resources with granular policies. Microsegmentation rules define each connection.
 Schedule a demo
Zero Trust access, data protection, CASB and UEBA in one platform. Each device proves its identity and applies security policies where work happens.
 Security console
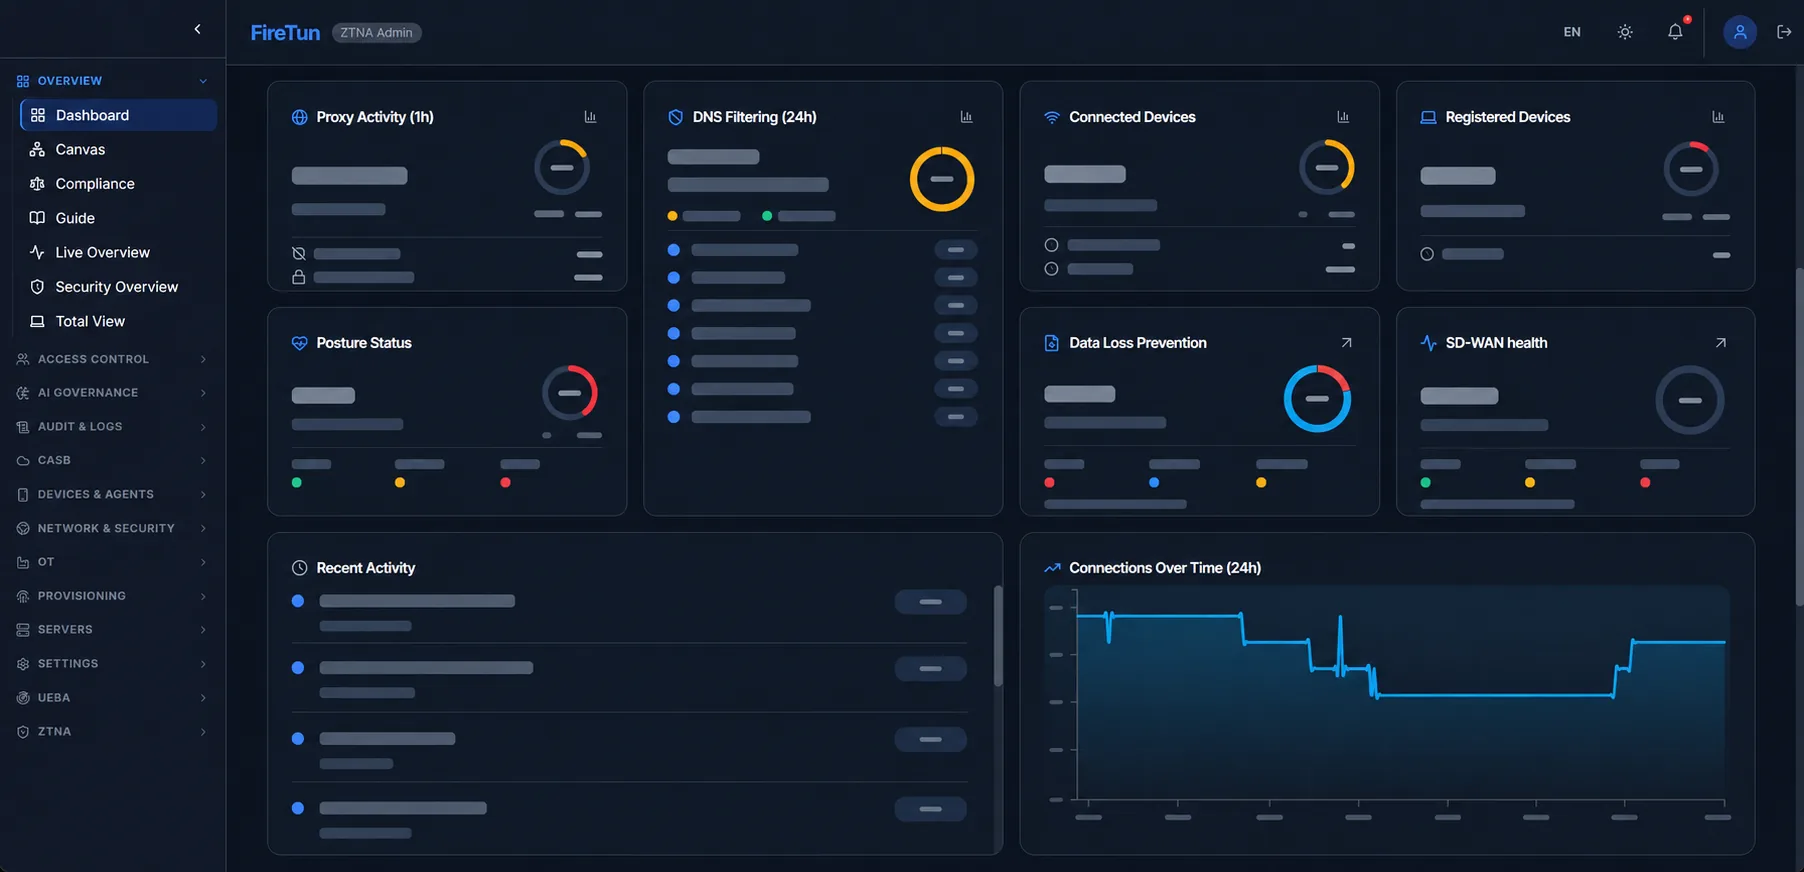
Desktop agent and FireTun console. Illustration.
The visual canvas connects users, authentication, controls and destinations. The platform distributes rules and the agent applies them on the device. Approved resources are reached over encrypted connections, using direct routes when the network allows it.
Identity, access policies and visibility in one place.
Posture, web and data protection, and local rules follow the device.
Each person reaches only the resources allowed by policy.
Controls on the device let traffic take a direct route to an approved resource when possible, while keeping access and protection rules in place.
FireTun combines access, local protection and operational signals to preserve context throughout the journey.
Connect users, groups, posture and resources with granular policies. Microsegmentation rules define each connection.
The agent checks security conditions before connecting and during use. Policy defines what happens when a check fails.
Web filtering, sensitive data protection and AI service policies, with visibility into usage and findings.
Device health, access events and alerts brought together for operations teams.
Review activity, findings, OAuth permissions and files from connected services (CASB).
Find changes in users, devices and executables and see the signals behind each detection (UEBA).
Observe conversations, assets and findings across industrial networks (OT).
Measure the health of available paths and review routing decisions (SD-WAN).
The console brings together access, device status, data protection and findings to guide daily operations.
On compatible devices, FireTun verifies that the identity credential belongs to the registered hardware. When connecting, the device proves it holds that identity; its posture provides current context for the access decision.
Device evaluation
Conceptual example of a device evaluation.
Connect people and resources with a consistent policy in the office, at home and on the move.
Define who can enter, which resources they can reach and under what conditions.
Combine access control, posture and data protection with visibility for the security team.
Let’s review your resources, users and security requirements in a guided demo.